End-to-End Encryption for Families: A Jargon-Free Guide
TL;DR: E2EE = only you hold the key to your data, the company can’t read it. Regular encryption = the company has a copy of the key. 60-second test: 3 questions for your family app.
Series: Clean Tech for Families · Article 3/6
End-to-end encryption (E2EE) means your data is encrypted with a key that only you hold — the company can’t read it, even if they wanted to. In this article, we explain in plain language how E2EE differs from regular encryption, why it matters for family data (health, finances, schedules), and how to check in 60 seconds whether your app actually offers it.
One Message, Your Entire Life on Display
You send your partner a message: “Emma has a pediatrician appointment Thursday at 3 PM, give her Advil at noon.”
Stop for a moment. That single message contains: your child’s name, medical information, schedules, medication habits. Now imagine that message landing on a company’s server like a postcard: the company that stores it can read it.
Now imagine it traveling in a sealed envelope. One that only you and the recipient have the key to.
That’s the difference between regular encryption and end-to-end encryption.
How Do Family Apps Encrypt Your Data?
Most family apps encrypt data “in transit.” That means your data is protected on the journey between your phone and the company’s server. But on the server itself? It sits there in plain text. The company has full access.
This isn’t malicious. It’s simply easier to build that way. Most companies do it like this.
But it’s worth understanding what that means in practice:
- In a server data breach — your family data is readable by the attacker.
- If a court order is issued — the company has to hand it over, because they can read it.
- If the privacy policy changes — data that was “safe” can change status overnight.
In January 2026, the Electronic Frontier Foundation launched the “Encrypt It Already” campaign — calling on six major tech companies (Meta, Apple, Google, Bluesky, Telegram, Ring) to implement true end-to-end encryption. Not because these companies are evil. Because the standard should be higher.
This isn’t about paranoia. It’s about raising the bar.
Pause
If you don’t have the energy to read about encryption right now — that’s OK. Bookmark this article. Come back when you’re ready. You don’t have to understand all of this in one sitting.
What Is End-to-End Encryption? A Simple Analogy
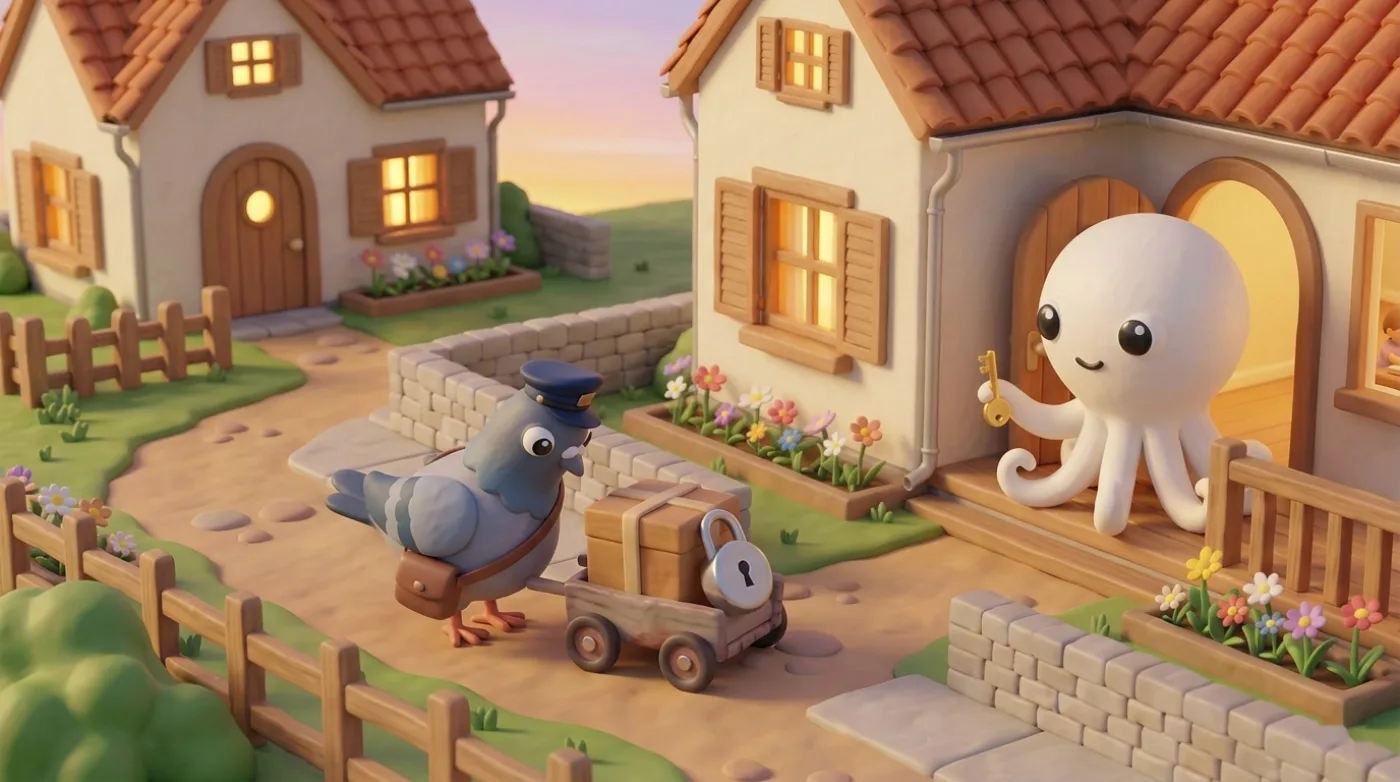
Imagine you’re sending a letter. Regular encryption (TLS) is like putting the letter in an envelope: nobody along the way can look inside, but at the post office, which is the company’s server, the envelope is opened and the letter sits there readable. You never see it happen.
E2EE is like a locked box where only the recipient has the key. The post office carries the box, but can’t look inside. Nobody reads your letter: not along the way, and not the post office itself.
That’s it. That’s the whole difference: who holds the key. If the company has a copy — it’s regular encryption. If only you hold the key — it’s E2EE.
Prefer a different image? Think of a safe deposit box at a bank. With regular encryption, the bank keeps a copy of the key. With E2EE — only you have the key. If you lose it, even the bank can’t open it. That’s the price of real security — but also its guarantee.
Why Does E2EE Matter for Family Data?
Family data isn’t vacation selfies. It’s:
- Children’s health — appointments, medications, allergies, diagnoses
- Finances — household budget, bills, obligations
- Schedules — who’s where, at what time, with whom
- Education — grades, needs, conversations with teachers
Taken together, this data paints a complete picture of your family’s life. More detailed than anything you’d find in any single place.
That’s why it’s worth asking: who else has access to that picture?
How Does E2EE Work in Practice?
Apps that take E2EE seriously work like this:
- The encryption key is generated on your device. It is created on your side, not on the company’s server.
- The server never sees this key. It stores encrypted data, but can’t read it.
- A recovery key is your choice. You can create one (e.g., a 24-word phrase) to regain access on a new device. But it’s your decision, not a requirement.
Examples of apps that take E2EE seriously:
- Signal — a messenger with E2EE from the very first message
- Proton Mail — email with zero-knowledge encryption
- ParentOS — a family operating system with end-to-end encryption for selected modules: finances, health records, calendar, tasks, shopping, meals, education and wellbeing. The server stores this data as ciphertext and can’t read it, though it still sees some metadata (dates, family member, category). Not everything is covered by E2EE: medication names and doses, routines and rewards are not, and integration data (Google or Outlook calendar, mail, bank) passes through our server on every platform.
How to Check If Your App Has E2EE: A 60-Second Test
You don’t need to understand cryptography. Just three questions. Open the FAQ or privacy policy of your family app and check:
| # | Question | Where to look |
|---|---|---|
| 1 | Does the app say “end-to-end encrypted”? | FAQ, Privacy Policy, Settings |
| 2 | Does the company state “we cannot read your data” or “zero-knowledge”? | Privacy Policy, Security page |
| 3 | Do you have a key/password that the company does NOT know? | Account settings, Security |
Your Score
| Answers | What it means |
|---|---|
| 3x Yes | True E2EE. Still check which data it covers. |
| 1-2x Yes | Partial encryption. Worth asking the company what exactly they encrypt. |
| 0x Yes | No E2EE. The company has access to your data. That’s not necessarily bad — but it’s worth knowing. |
Share this test with another person in your household. Check one app together — the one where you store your family’s health or financial data. Asking one question is already more than most of us do.
One Micro-Step for Today
Check one thing: go into the privacy settings or FAQ of your most important family app. Look for the words: “end-to-end encrypted,” “zero-knowledge,” “only you can read your data.”
If you can’t find them — that doesn’t mean the app is bad. It means it’s worth knowing what standard it offers.
Don’t have the energy right now? That’s fine. Bookmark this article and come back when you have a moment.
Related Articles in This Series
- Article 1: If You’re Not Paying, You’re the Product. What About Your Child? — how to identify what you’re really paying for in “free” apps
- Article 2: Organic Software: How to Read an App’s Ingredient Label — how to assess what an app actually does with your data
Frequently Asked Questions
How is E2EE different from regular encryption?
Regular encryption (TLS) protects data in transit — between your phone and the server. But on the server itself, the data sits in plain text — the company can read it. E2EE means only you hold the encryption key. The server stores encrypted data but cannot read it. Even in a data breach, the data is useless without your key.
Is E2EE hard to use?
No. In well-designed apps (e.g. Signal, Proton), encryption works automatically from day one. The key is generated on your device. In ParentOS the family key is also created on the device and never sent to the server.
What happens if I lose my encryption key?
This is the one trade-off with E2EE. If you lose your key and don’t have a recovery key — the data is gone. That’s why good apps offer a 24-word recovery phrase. In ParentOS you add a new device by pairing it via QR code with an existing one, or with that phrase. If you lose the phrase and all your devices, ParentOS cannot recover the data.
Series “Clean Tech for Families”:
- Article 1: If You’re Not Paying, You’re the Product. But What About Your Child?
- Article 2: Organic Software: How to Read an App’s Ingredient Label
- Article 3: End-to-End Encryption for Families: A Jargon-Free Guide (this article)
- Article 4: Slow Tech: When Technology Slows Down Instead of Speeding Up
- Article 5: What Does Your Child’s Learning App Know About Them?
- Article 6: I Installed OpenClaw. Then I Checked What It Had Access To.
- Article 7: Who Sees Your Family’s Data? 7 Layers You Shouldn’t Have to Think About
- Article 8: Digital Kidnapping: What Actually Happens to the Photos You Share
Sources:
- Electronic Frontier Foundation, “Encrypt It Already” campaign (2026)
- Signal Foundation, Signal Protocol documentation
- ParentOS, Device Key E2EE Architecture
Calm families start with awareness.